
Confidential computing
Confidential computing protects sensitive data while software is processing it. Computation takes place in a hardware-based trusted execution environment, or TEE, designed to isolate the workload from the host operating system and privileged administrators. This complements encryption during storage and transmission by protecting information at the point when an application needs to use it.
Confidential computing can allow organizations to run sensitive workloads on shared or rented infrastructure while limiting access by the infrastructure operator. Banks can use the approach for workloads such as fraud analysis or cryptographic key processing, where exposing the underlying data would create a security risk. Hardware isolation and verification of the execution environment are important parts of the protection, alongside the wider controls used for operational resilience.
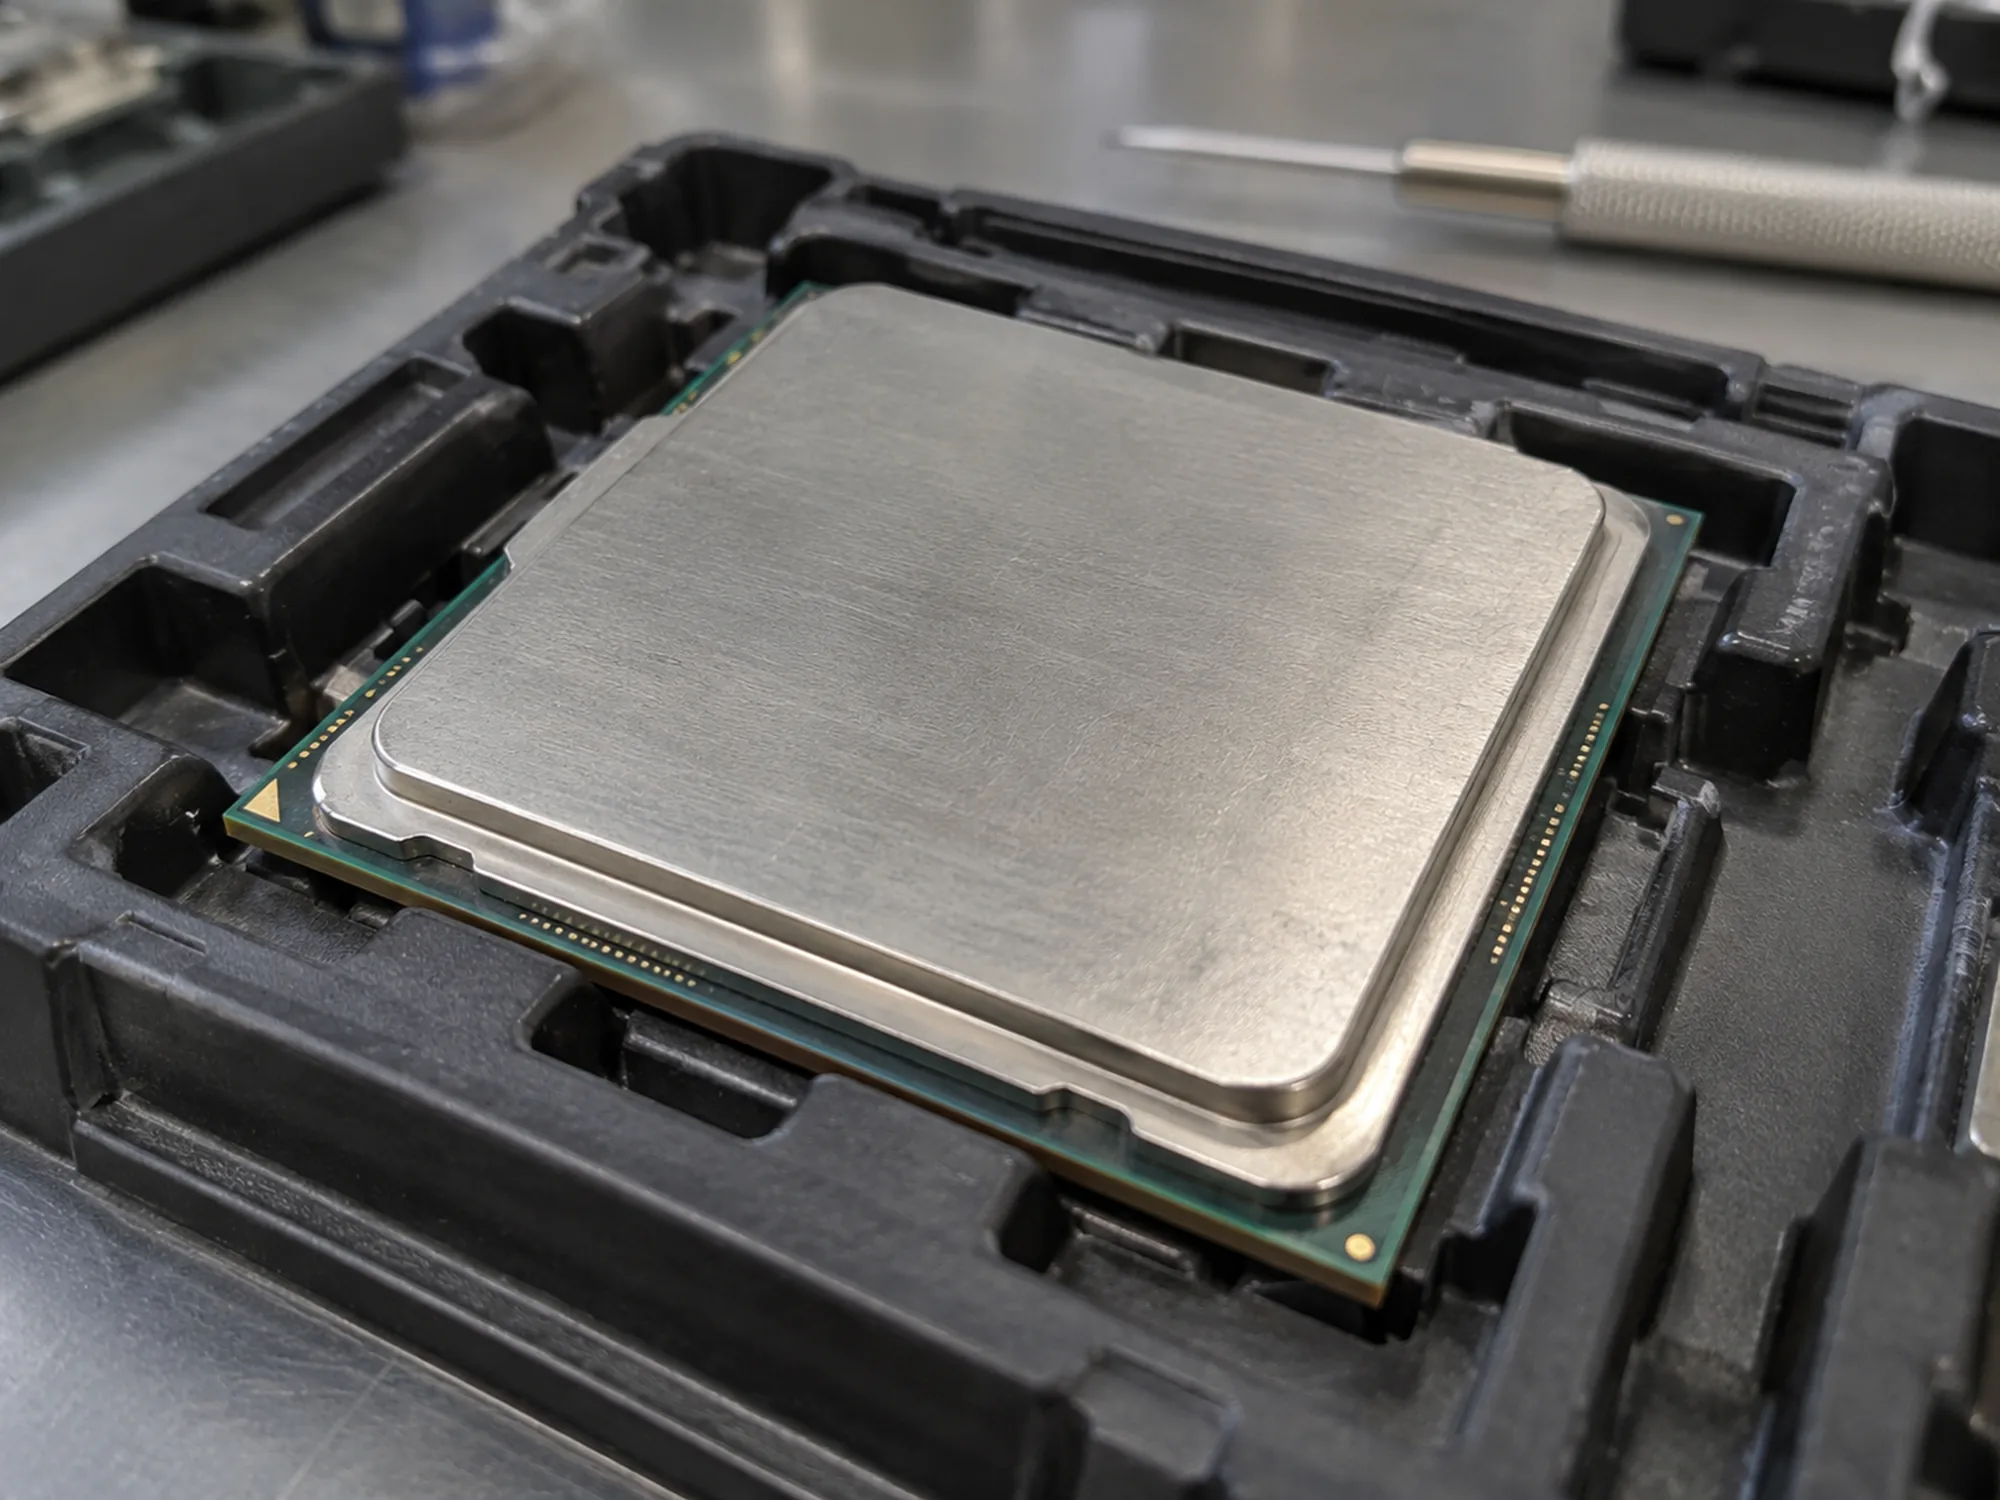
How trusted execution environments work
The processor encrypts the memory of the TEE with keys that never leave the chip. Intel SGX, introduced in 2015, isolates single application enclaves. Intel TDX and AMD SEV-SNP protect whole virtual machines, so existing software can run confidentially without a rewrite, and Arm has a matching design called CCA. Nvidia brought the model to GPUs with the H100, which matters for AI workloads.
Remote attestation makes the protection checkable. Before a TEE receives keys or data, it proves to the other party, signed by the chip, which code is running and on what hardware. A bank can therefore release a decryption key only to a workload whose code it has approved. The Confidential Computing Consortium, founded in 2019 under the Linux Foundation, works on common standards for these steps.
Where finance uses confidential computing
Swift and Google Cloud announced in December 2024 an anti-fraud model trained with federated learning and confidential computing. Each of the 12 participating financial institutions keeps its transaction data, and the shared model learns from it inside TEEs, so no bank sees another bank's data. Rhino Health and Capgemini are technology partners in the project.
In digital assets, Fireblocks runs the key shares of its multi-party computation wallets inside Intel SGX enclaves, so a compromised server does not expose the key material. Banks that hold crypto assets for clients meet the technique through such custody platforms and next to hardware security modules, see HSMs for crypto assets.
What DORA and the ECB ask for data in use
The DORA technical standard on ICT risk management, Commission Delegated Regulation (EU) 2024/1774, requires in Article 6 an encryption policy that covers data at rest, in transit and, where relevant, in use. Where encrypting data in use is not possible, the financial entity processes it in a separated and protected environment. The guide on cloud outsourcing from the ECB asks banks to encrypt data in use where feasible.
Neither text names confidential computing, but confidential computing is one way to meet the requirement, and the bank documents how the TEE, the attestation and the key release fit its encryption policy.
Limits of the technique
A TEE moves trust from the cloud provider to the chip maker. Researchers have shown side-channel attacks on Intel SGX, such as SGAxe in 2020 and ÆPIC Leak in 2022, that extracted data from enclaves before patches closed them. A bank that relies on confidential computing therefore tracks firmware updates and attestation results as part of its vulnerability management.
Upcoming events on digital infrastructure
What is confidential computing?
Confidential computing is the protection of data during processing in a hardware-based trusted execution environment. The data is decrypted only inside the TEE, and code outside it, including the cloud provider's software, cannot read it.
Which cloud providers offer confidential computing?
Microsoft Azure, Amazon Web Services and Google Cloud offer confidential virtual machines based on AMD SEV-SNP or Intel TDX, and AWS also has its own Nitro Enclaves. Azure offers confidential GPU virtual machines with Nvidia H100 chips for AI workloads.
How does confidential computing differ from homomorphic encryption?
Homomorphic encryption computes on data that stays encrypted throughout, using mathematics alone, and needs no trust in a chip vendor. Homomorphic encryption is far slower for most workloads. Confidential computing decrypts the data inside protected hardware and runs at close to normal speed, but it depends on the chip maker's design and patches.
Confidential computing and Finance Loop
Finance Loop covers confidential computing in its Digital Infrastructure & Sovereignty track, where security architects from banks and custody firms meet the cloud and chip companies that build TEEs. Finance Loop offers a provider a sponsored webinar to show banks an attested workload running in production.
Finance Loop is a professional network supporting the institutional use of emerging technologies in finance, such as AI, digital payments, cloud and blockchain solutions. Finance Loop helps its members build skills and personal networks in these fields: Investment & Digital Assets, Payments & Digital Money, Digital Infrastructure & Sovereignty, and Risk & Compliance.