
The Legal Entity Identifier: twenty characters that name a counterparty
If a trade report has to say who the counterparty was, something has to name that company unambiguously, across borders and across the dozen internal systems that each spell it differently. The Legal Entity Identifier is that something: a 20-character alphanumeric code for one legal entity, usable by anyone, free to look up.
Below: how the code is built and which standard defines it, why the question was unanswerable in 2008, the three layers that issue and govern it, which European reporting duties consume it, why a lapsed record stops a report, and what the cryptographically verifiable version adds.
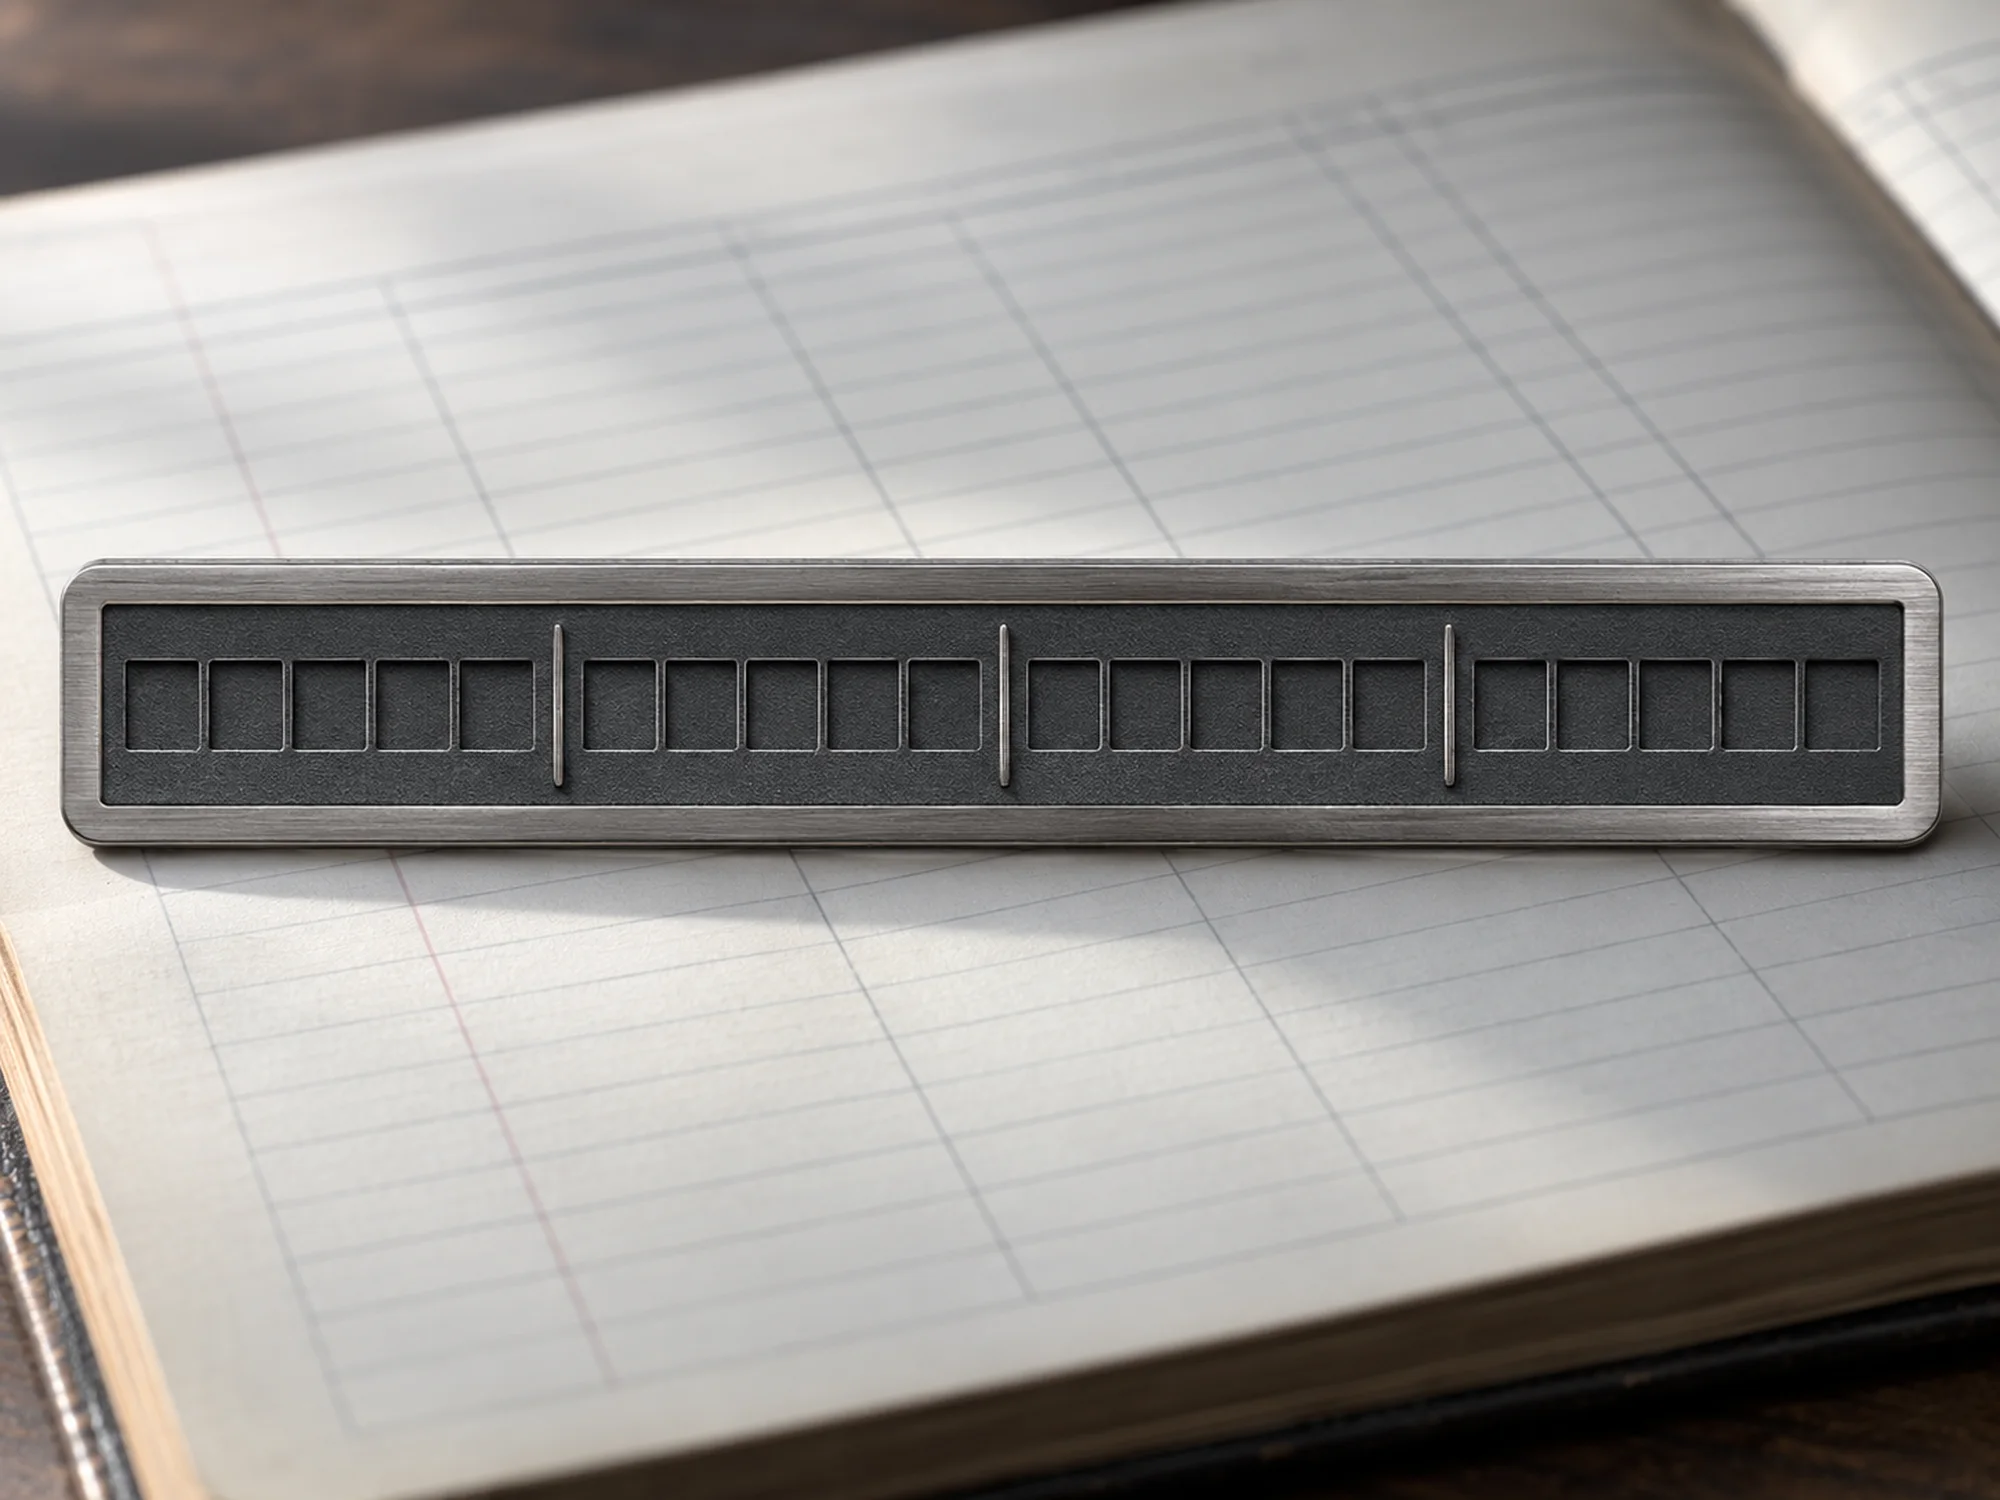
A 20-character code, defined by ISO 17442
The Global Legal Entity Identifier Foundation, GLEIF, describes the LEI as a unique 20-character alphanumeric code that lets anyone, anywhere, access clear identification data about a legal entity. The standard behind it is ISO 17442, which establishes four principles for the identifier: it is global, it assigns a single unique identifier per entity, it rests on high-quality data, and it is a public good that anyone may use free of charge.
Inside the 20 characters, as the reference description of the code sets out, the first four characters identify the issuing Local Operating Unit, the middle section is the string that unit assigned to the entity, and the final two are checksum digits computed with MOD-97-10. The last point has a practical use: a typo in an LEI usually fails the checksum, so a validation routine catches it before the report leaves the building.
Why the question was unanswerable in 2008
When a large counterparty failed, supervisors and the firms themselves could not say quickly how much exposure sat where, because there was no common name for a legal entity. One institution's "ABC Bank plc London" was another's "ABC Bank PLC, Branch UK", and neither mapped reliably to a legal person with an address and a parent. Aggregating exposure across firms meant reconciling names by hand.
The identifier was developed by the G20 in 2011 in direct response to that inability, with the Financial Stability Board establishing the governance framework and the G20 endorsing the LEI Charter in 2012, which created the Regulatory Oversight Committee and the Global LEI System. That origin explains the design: a public good, free to look up, because the point was aggregation across the system and not a commercial data product.
Three layers: oversight, foundation, issuers
The LEI Regulatory Oversight Committee is the decision-making body for the system under the Financial Stability Board, setting the policies that govern data access and use. GLEIF operates the system, accredits the issuers and publishes the data. The Local Operating Units, which GLEIF also calls LEI Issuers, are the organizations that actually issue codes.
GLEIF describes those issuers as supplying registration, identity verification, renewal and other services, and acting as the primary interface for a legal entity that wants an LEI, and it is explicit that an entity is not limited to an issuer in its own country: it can use any issuer accredited for its jurisdiction. Two further roles sit around them. Registration Agents help entities reach the issuer network, and Validation Agents are financial institutions that obtain and maintain LEIs for their clients through their existing onboarding procedures. The issuers charge for registration and renewal; GLEIF publishes the list of accredited issuers, and this page ranks none of them.
Which European reporting duties consume an LEI
The code is not an administrative nicety for a firm in scope of European transaction reporting. Reporting under MiFIR for transactions in financial instruments, under EMIR for derivatives and under SFTR for securities financing all identify the parties by LEI, and ESMA publishes the reporting guidance that spells out the fields.
The operational consequence is the rule firms repeat as "no LEI, no trade": an investment firm that cannot identify a client by LEI cannot submit a complete report for that transaction, so the onboarding process has to collect the code before the business, not after. Capital markets in Frankfurt covers the trading side this reporting attaches to.
The renewal duty, and why a lapsed record blocks a report
An LEI is not issued once and forgotten. The registration is valid for one year from the date of registration, and annual renewal is required for an entity that wants to keep participating in regulated financial transactions. Renewal means the reference data is re-verified, which is what keeps the register worth using.
A record that was not renewed goes to a lapsed status, and that is where the operational pain lives. The code still exists and still looks correct in your database, so nothing in your systems objects, and the report is rejected or flagged downstream because the counterparty's record is stale. The fix is a monitoring process that watches the renewal dates of the LEIs you depend on, including your clients' and your counterparties', not only your own. A firm acting as a Validation Agent carries that maintenance for its clients by design.
The verifiable LEI, and who may sign for the entity
An LEI tells you which company. It does not tell you that the person emailing you may act for it, which is the gap that payment fraud and contract fraud live in. GLEIF's answer is the verifiable LEI, the vLEI, a credential form of the identifier in a digital trust ecosystem.
GLEIF defines a set of credentials in it: a Legal Entity vLEI Credential issued by a Qualified vLEI Issuer to the entity, an Official Organizational Role credential for official representatives of that entity, an Engagement Context Role credential for representatives in functional or other contexts, plus credentials for the issuers themselves and an Authorization credential for instructing issuance and revocation. The role credentials are the interesting part for a bank, because they move the question from "which company is this" to "may this named person act for it", which is a different and harder check.
GLEIF is seated in Frankfurt
GLEIF was established in 2014 under Swiss law and set up its office in Frankfurt the same year, later adding offices for the Americas, Japan and Singapore. The body that runs the global identifier for legal entities therefore works in the same city as the institutions reporting with it, which is why entity data turns up as a subject at Frankfurt events and not only in a standards committee.
Finanzplatz Frankfurt am Main covers the wider financial center, and the data-services side of the city sits on WM InnoLab by WM Datenservice. The identifier for instruments, as opposed to entities, is a separate system, covered by the Digital Token Identifier Foundation.
From the entity code to the people behind it
An LEI answers which legal person you are dealing with, and an anti-money laundering duty then asks who ultimately owns and controls that person. The two fit together: the code gives the ownership-chain walk a stable identifier for each layer, which is exactly what makes a corporate structure traceable instead of a set of similar names.
Know your business verification covers that process, the beneficial owner definition and the German Transparenzregister. KYC in Germany and anti-money laundering in Germany cover the duties around both.
What is an LEI code?
A 20-character alphanumeric code that identifies one legal entity globally, defined by ISO 17442 and operated as a public good whose data anyone can look up free of charge. The first four characters identify the issuing Local Operating Unit and the last two are checksum digits.
Who needs an LEI?
Any legal entity that is a party to transactions under European reporting regimes such as MiFIR, EMIR and SFTR, which in practice means companies, funds and other entities trading financial instruments, including as a client of an investment firm. A firm that cannot identify its client by LEI cannot file a complete transaction report, which is why the code is collected during onboarding.
Does an LEI expire?
The registration is valid for one year from registration and has to be renewed annually to stay current. The code itself is not withdrawn, but an unrenewed record goes to a lapsed status, and a lapsed counterparty record is what causes a report to be rejected or flagged even though the code in your system looks correct.
What is a vLEI?
The verifiable LEI: a cryptographically verifiable credential form of the identifier, issued in GLEIF's vLEI ecosystem. Alongside the entity credential it defines role credentials, the Official Organizational Role and the Engagement Context Role, which bind a named person to the entity and answer who may act for it.
The Legal Entity Identifier and Finance Loop
Finance Loop is where the reporting teams chasing a lapsed counterparty record meet the data people who maintain the entity master. Finance Loop is the meeting place for entity data and reporting in Frankfurt, the city where GLEIF itself is seated, with meetups and conferences on market data, compliance technology and digital identity. Finance Loop keeps those dates in its event calendar.
Finance Loop is a professional network and has the goal of driving the adoption of emerging technologies in finance, such as AI, tokenization, stablecoins, and DeFi. Finance Loop helps its members build skills and personal networks in these fields: Investment & Digital Assets, Payments & Digital Money, Digital Infrastructure & Sovereignty, and Risk & Compliance.